Transform Your Cybersecurity Posture
A complete toolkit for managers, security officers and non-executive directors.
Get Started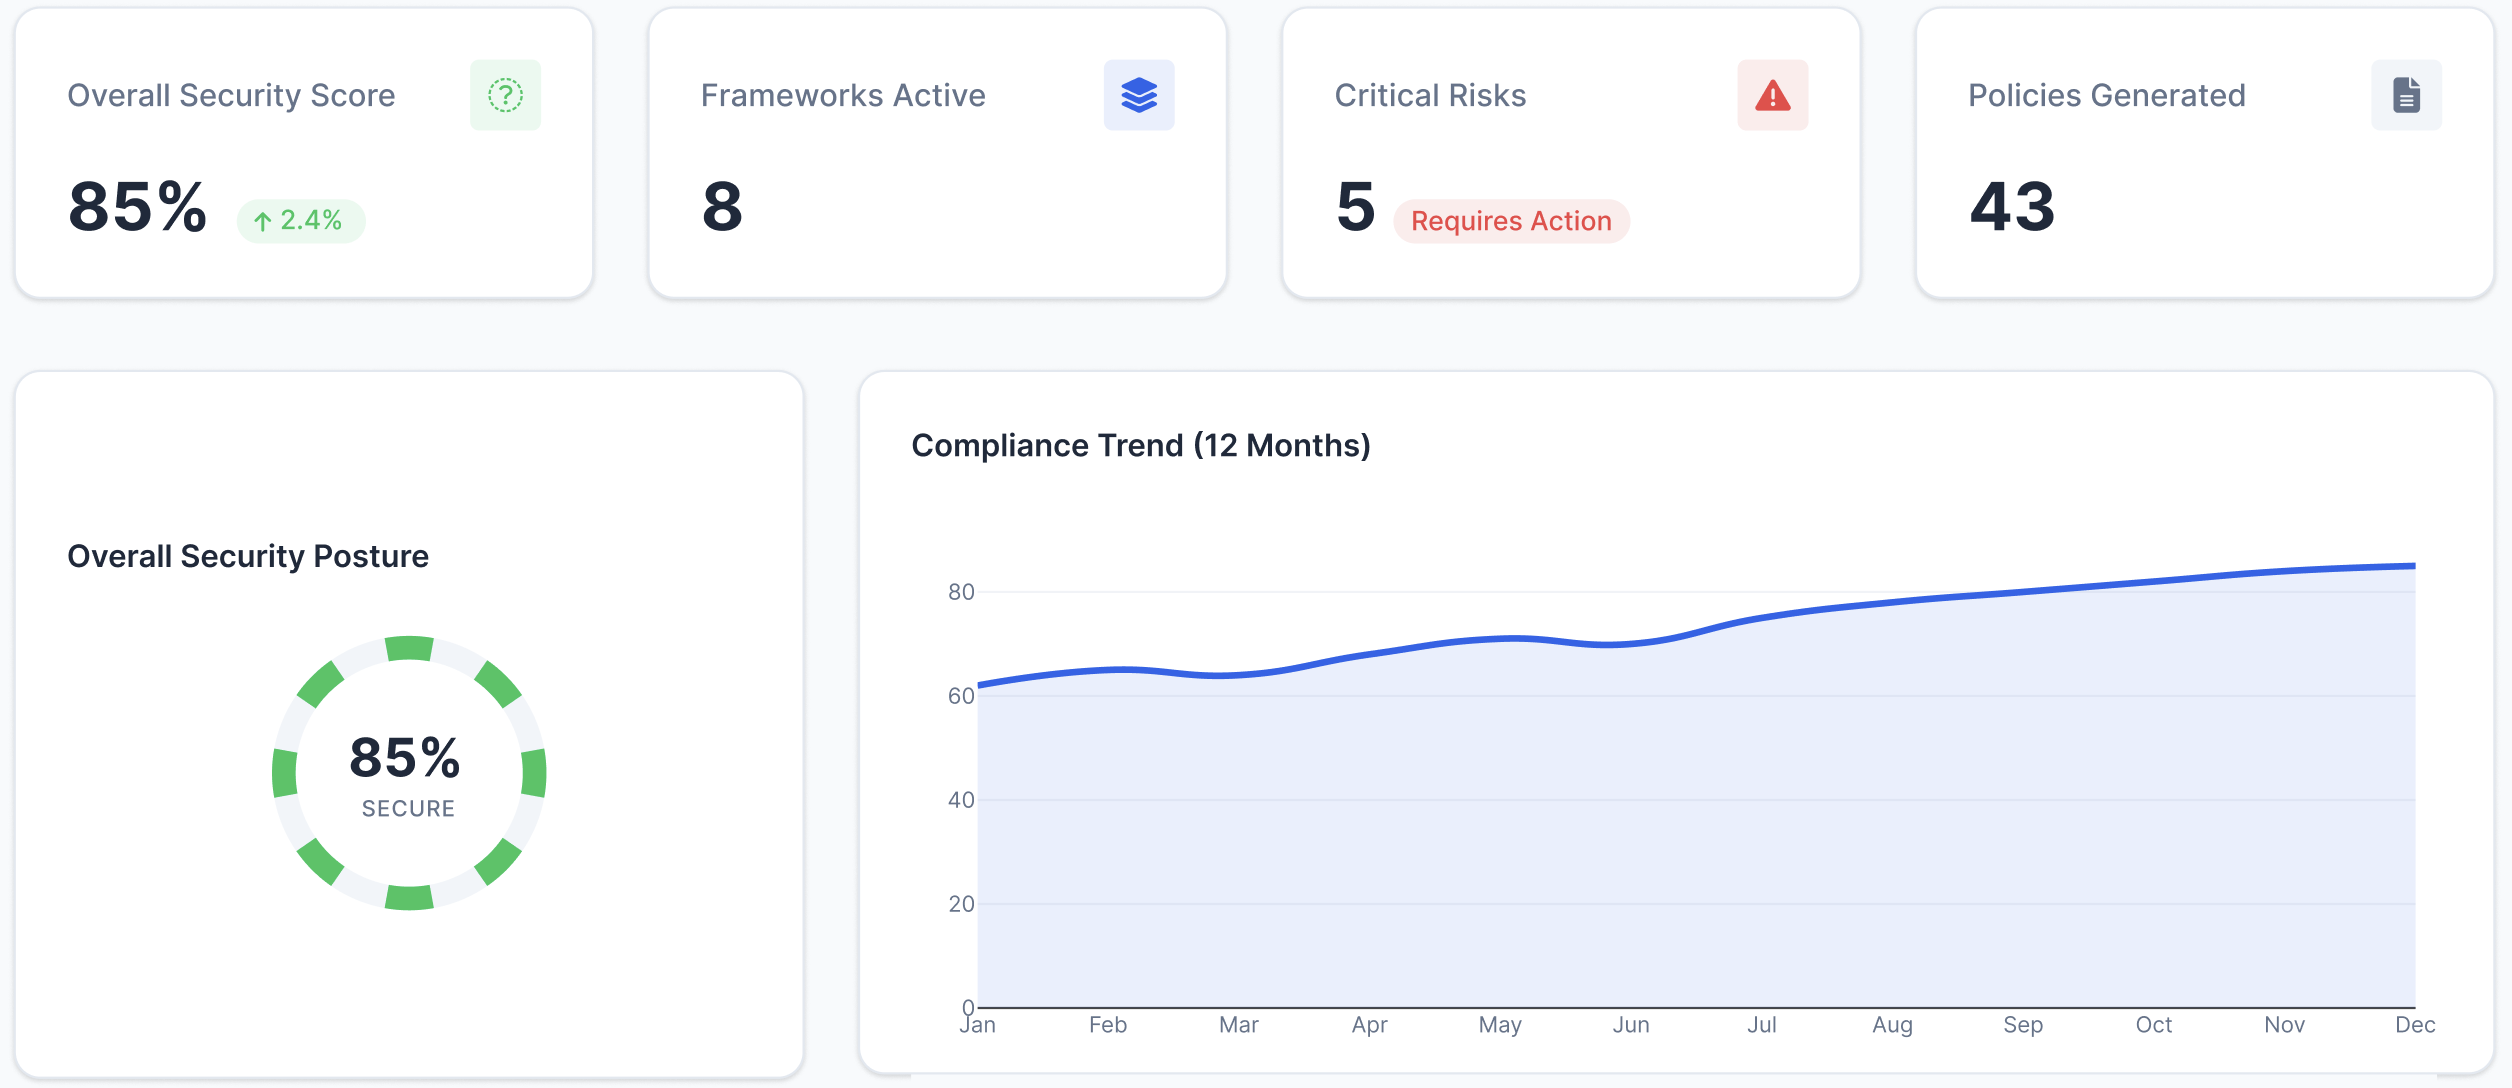
Everything you need to stay digitally resilient
A complete toolkit for managers, security officers and non-executive directors
Track Your Compliance
Monitor your organisation’s compliance posture in real time.
Layered Security Insights
Understand your security maturity across multiple domains.
Policy Management
Keep your policies updated and aligned with ISO 27001.
Add New Controls Easily
Expand your control library with ease.
Visualise Risk
See risk trends and insights instantly.
Cloud Ready
Access your compliance dashboard anywhere.
Leverage certification frameworks to improve your cybersecurity posture
1
Assess
Assess your organisation’s cybersecurity posture in a central, structured way to measure current controls against the ISO 27001 information security standard. Understand your organisations cybersecurity stance through risk assessment, identify gaps in policies and technical controls, assign control owners and improvement actions, collect evidence of compliance, and track progress through dashboards and reports. Assessment is the first step for management and the board to understand both the organisation’s current level of security maturity and the priority actions needed to reduce cyber risk.
2
Report
Report your organisation’s cybersecurity posture through clear dashboards, risk registers and board-ready reports that show how well the organisation’s controls align with ISO 27001 requirements. Summarise the status of key controls, outstanding risks, incidents, audit findings, policy compliance, supplier assessments and remediation actions, including who is responsible and whether actions are on track. Reporting is the second step and gives management and the board a timely view of the organisation’s security maturity, areas of exposure and progress in strengthening cyber resilience.
3
Improve
Improve your organisation’s cybersecurity posture by comparing its existing policies, processes and technical controls against the requirements of the ISO 27001 standard. Highlight control gaps, such as incomplete access reviews, missing incident response testing, weak supplier assessments, outdated policies or insufficient staff training, and turn them into prioritised improvement actions. Each action can be assigned to an owner, given a due date and risk rating, supported by evidence requirements, and tracked through to completion. This final step creates a practical, transparent improvement plan that helps management focus resources on the areas that will most effectively reduce cyber risk.
Real-time Compliance Trend
Frequently Asked Questions
How do I create an organisation?
For more information see the about page where each step of registering and establishing your organisation with the platform is set out.
Which cybersecurity frameworks does it support?
Currently ISO27001, with more coming soon.
How does this tool work?
We guide you through a detailed registration process where we are able to learn the specific nature of the risks associated with your business. Through choosing from one of our support frameworks for Governance, Regulation and Compliance, the platform will display a corresponding risk assessment and produce a curated set of controls. When fully registered, the platform will provide differing levels of easy to access organisation wide assessment of the level of implementation of the framework, produce corresponding reports of such as well as through our system's AI powered analysis, provide improved policy recommendations.
Can I get a discount if I am a Not-for-profit?
Yes, please contact us with your details.